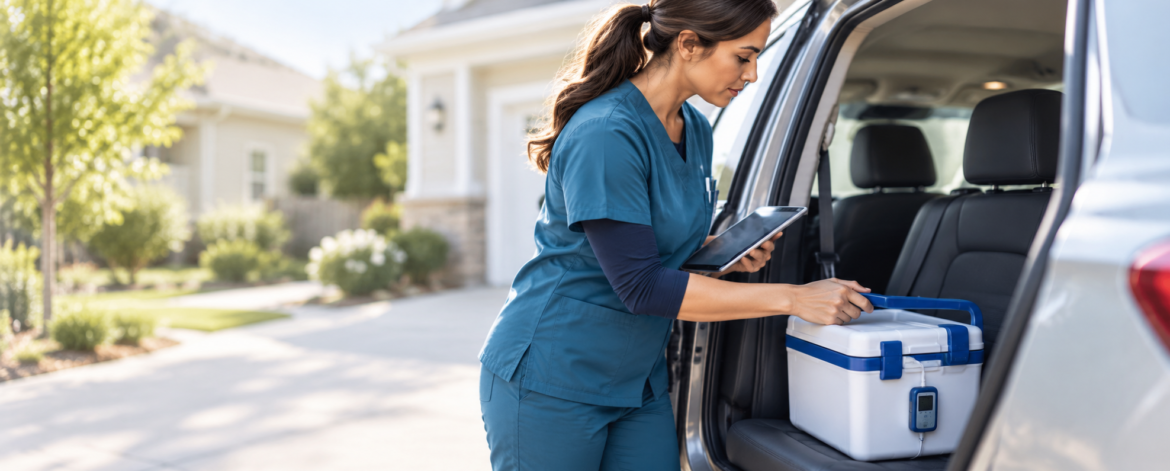
Key Takeaways Direct-to-patient medication delivery was supposed to take the agency out of the logistics business. In practice, home health clinicians still end up moving medications. A delivery goes to the wrong address, a refill is needed before the next shipment,…
How Long Must a Hospice Keep Patient Records After a Death?
How long must a hospice keep patient records is a question with more than one answer running at the same time, and for California agencies the answer changed in June 2026. A federal floor sits under every Medicare-certified hospice, a longer…
How to Train Hospice Volunteers on HIPAA
This guide covers why a hospice has to train volunteers on HIPAA, how to build and document the program yourself in five steps, and how IT Total Care supports the access control, device management, and evidence that sit underneath it. 1….
Does HIPAA Apply to Home Care Agencies?
Whether HIPAA applies to home care agencies is decided by a two-part test, and most published guidance only runs the first half of it. That matters because the answer changes what an agency has to document, who can enforce against it,…
How to Meet California’s 30-Day Breach Notification Deadline
At 4:40 on a Friday afternoon, an office coordinator at a home care agency in the East Bay opens the shared drive to pull the weekend’s care plans and finds every file renamed. She calls the owner, who calls the person…
Can You Outsource the HIPAA Security Officer Role to Your IT Provider?
Can you outsource the HIPAA security officer role along with the rest of your technology? It is the question that produces the longest pause when a surveyor asks a home health administrator to name the agency’s Security Official. Agencies that handed…
How to Build a HIPAA Shared Responsibility Matrix With Your IT Provider
A HIPAA shared responsibility matrix answers a question most home health agencies cannot answer on the spot: who owns each compliance function, the agency or the IT provider. Ask an administrator who approves the risk analysis and you will usually get…
Is a Stolen Encrypted Laptop a Reportable HIPAA Breach?
Is a stolen encrypted laptop a reportable HIPAA breach? Usually not under federal law, and that answer holds only if the agency can prove three specific things about the device after it is already gone. For a California home health agency…
How to Report a Medical Information Breach to CDPH in 15 Business Days
This guide explains why reporting a medical information breach to CDPH matters for a California licensed agency, how to work through the filing step by step on your own, and how IT Total Care builds the detection and evidence the filing…